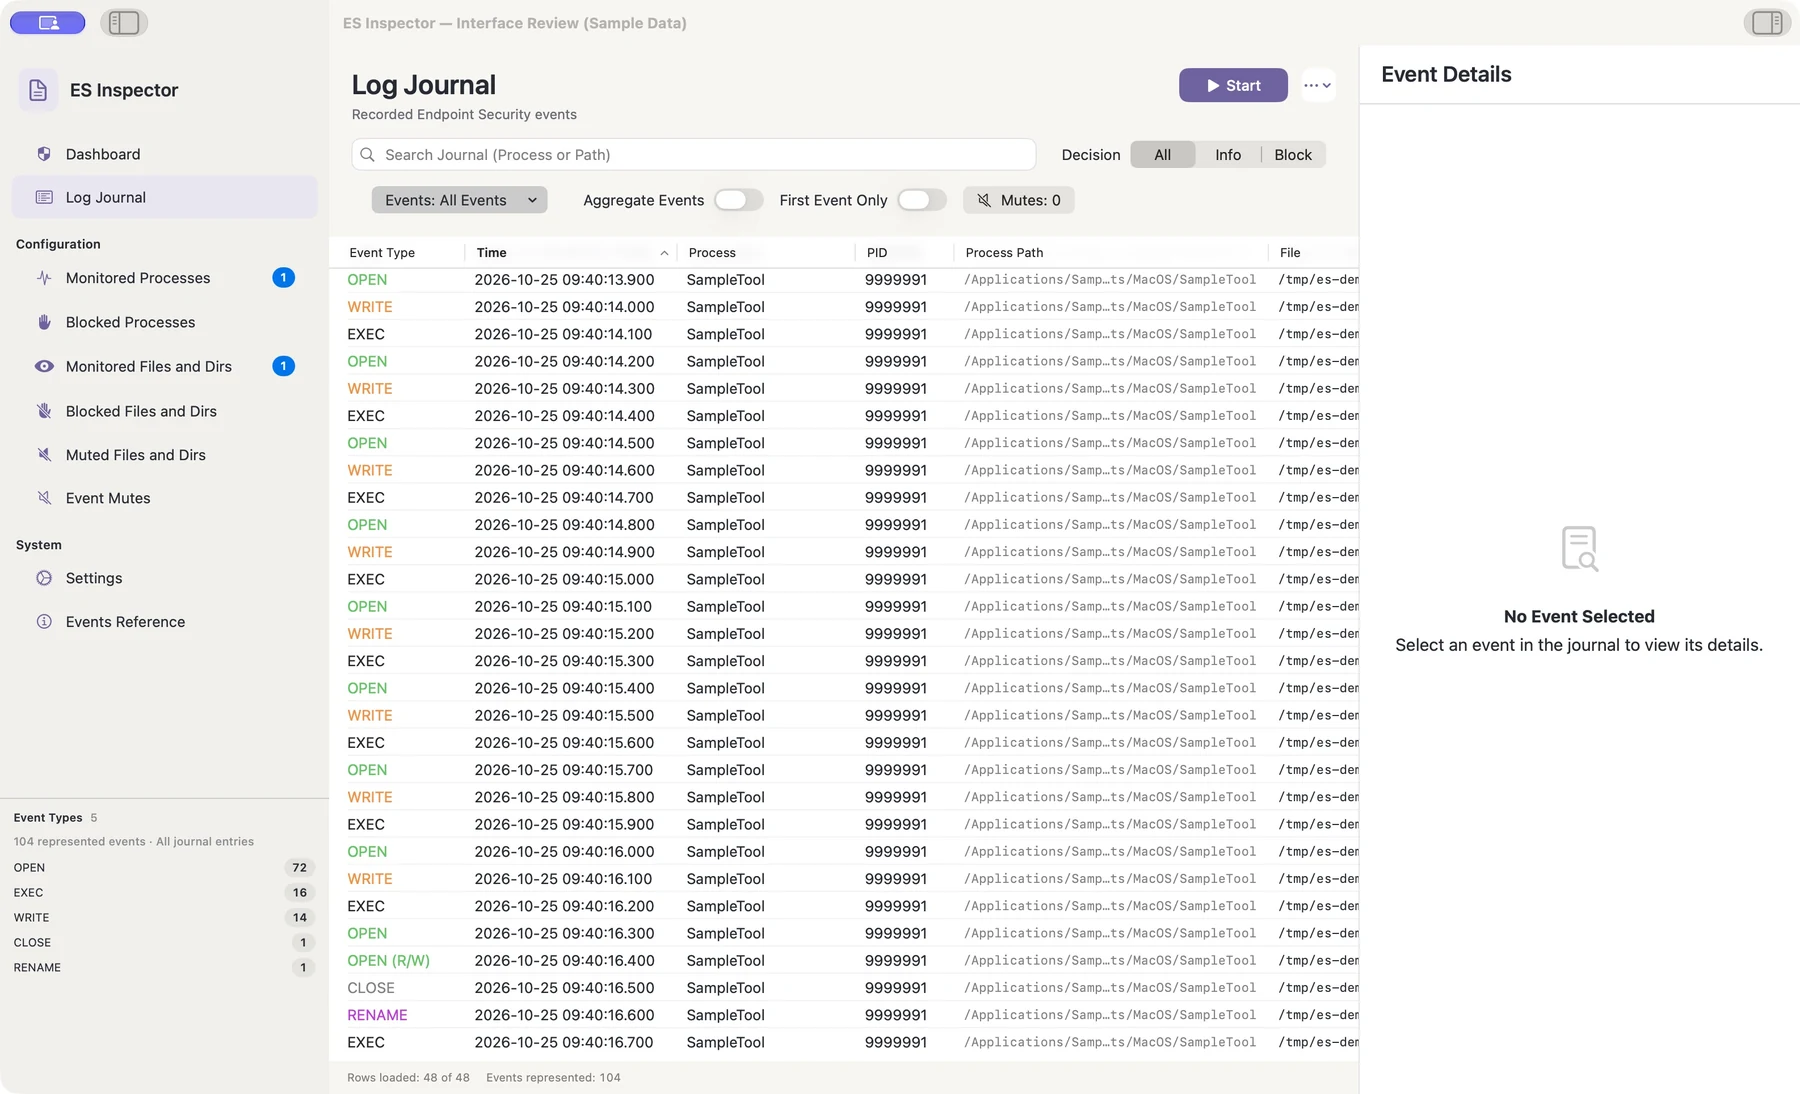
Follow the events
Filter captured events by type, process, path, and decision. Aggregate repeated activity when a sequence becomes noisy.
 Endpoint Security Inspector
Security research / macOS
See what happens beneath the app.
A native workspace for understanding how applications interact with macOS. Follow process and file events, inspect their details, and bring an investigation back to the rule that matters.
Available on request
01 / Why it exists
When an operation crosses executables, helpers, and files, the useful answer is often in the relationship between events. Endpoint Security Inspector combines a journal, process information, event filters, and explicit policies in one place.
Filter captured events by type, process, path, and decision. Aggregate repeated activity when a sequence becomes noisy.
Read complete event fields, process identities, parent relationships, arguments, and destination paths in the inspector.
Configure monitored and blocked targets and event mutes. Keep policy decisions alongside the activity they explain.
02 / A closer look
See the interface in detail.
Open any image to explore it.
03 / In practice
Configure the processes, files, and event types for your investigation.
Filter or aggregate events and select a record for full context.
Use event details and exports to support your diagnosis.
Configuration and event history are kept locally. Records can include paths, user and process identities, arguments, and environment data.
Capture uses a privileged Endpoint Security service. macOS requires the relevant entitlements and system permissions.
Diagnostic exports may contain sensitive system metadata. Review them before sharing. Capture does not make private fields public.
05 / Get started
This independent application is available on request. Tell me what you want to use it for and which device and OS version you have.
Request access ↗A question about the app?
Setup, everyday use, and a direct way to get help.
Help & support ↗Contact the developer ↗